


HHS skipped the HIPAA penalty inflation adjustment this year. Every penalty stays at its 2025 amount, OCR kept settling cases through 2026, and HIPAA Journal expects the 2027 adjustment to cover two years of inflation at once.
Missing data caused the freeze: HHS confirmed in an October 21 Federal Register notice that the 2025 government shutdown stopped the Bureau of Labor Statistics from producing the October inflation figures the annual adjustment depends on, so the 2025 amounts carry into 2026.
HIPAA penalty tiers stay at their 2025 amounts
HHS lists the four HIPAA penalty tiers in 45 CFR 102.3, and each tier scales with what the organization knew and how fast it fixed the problem.
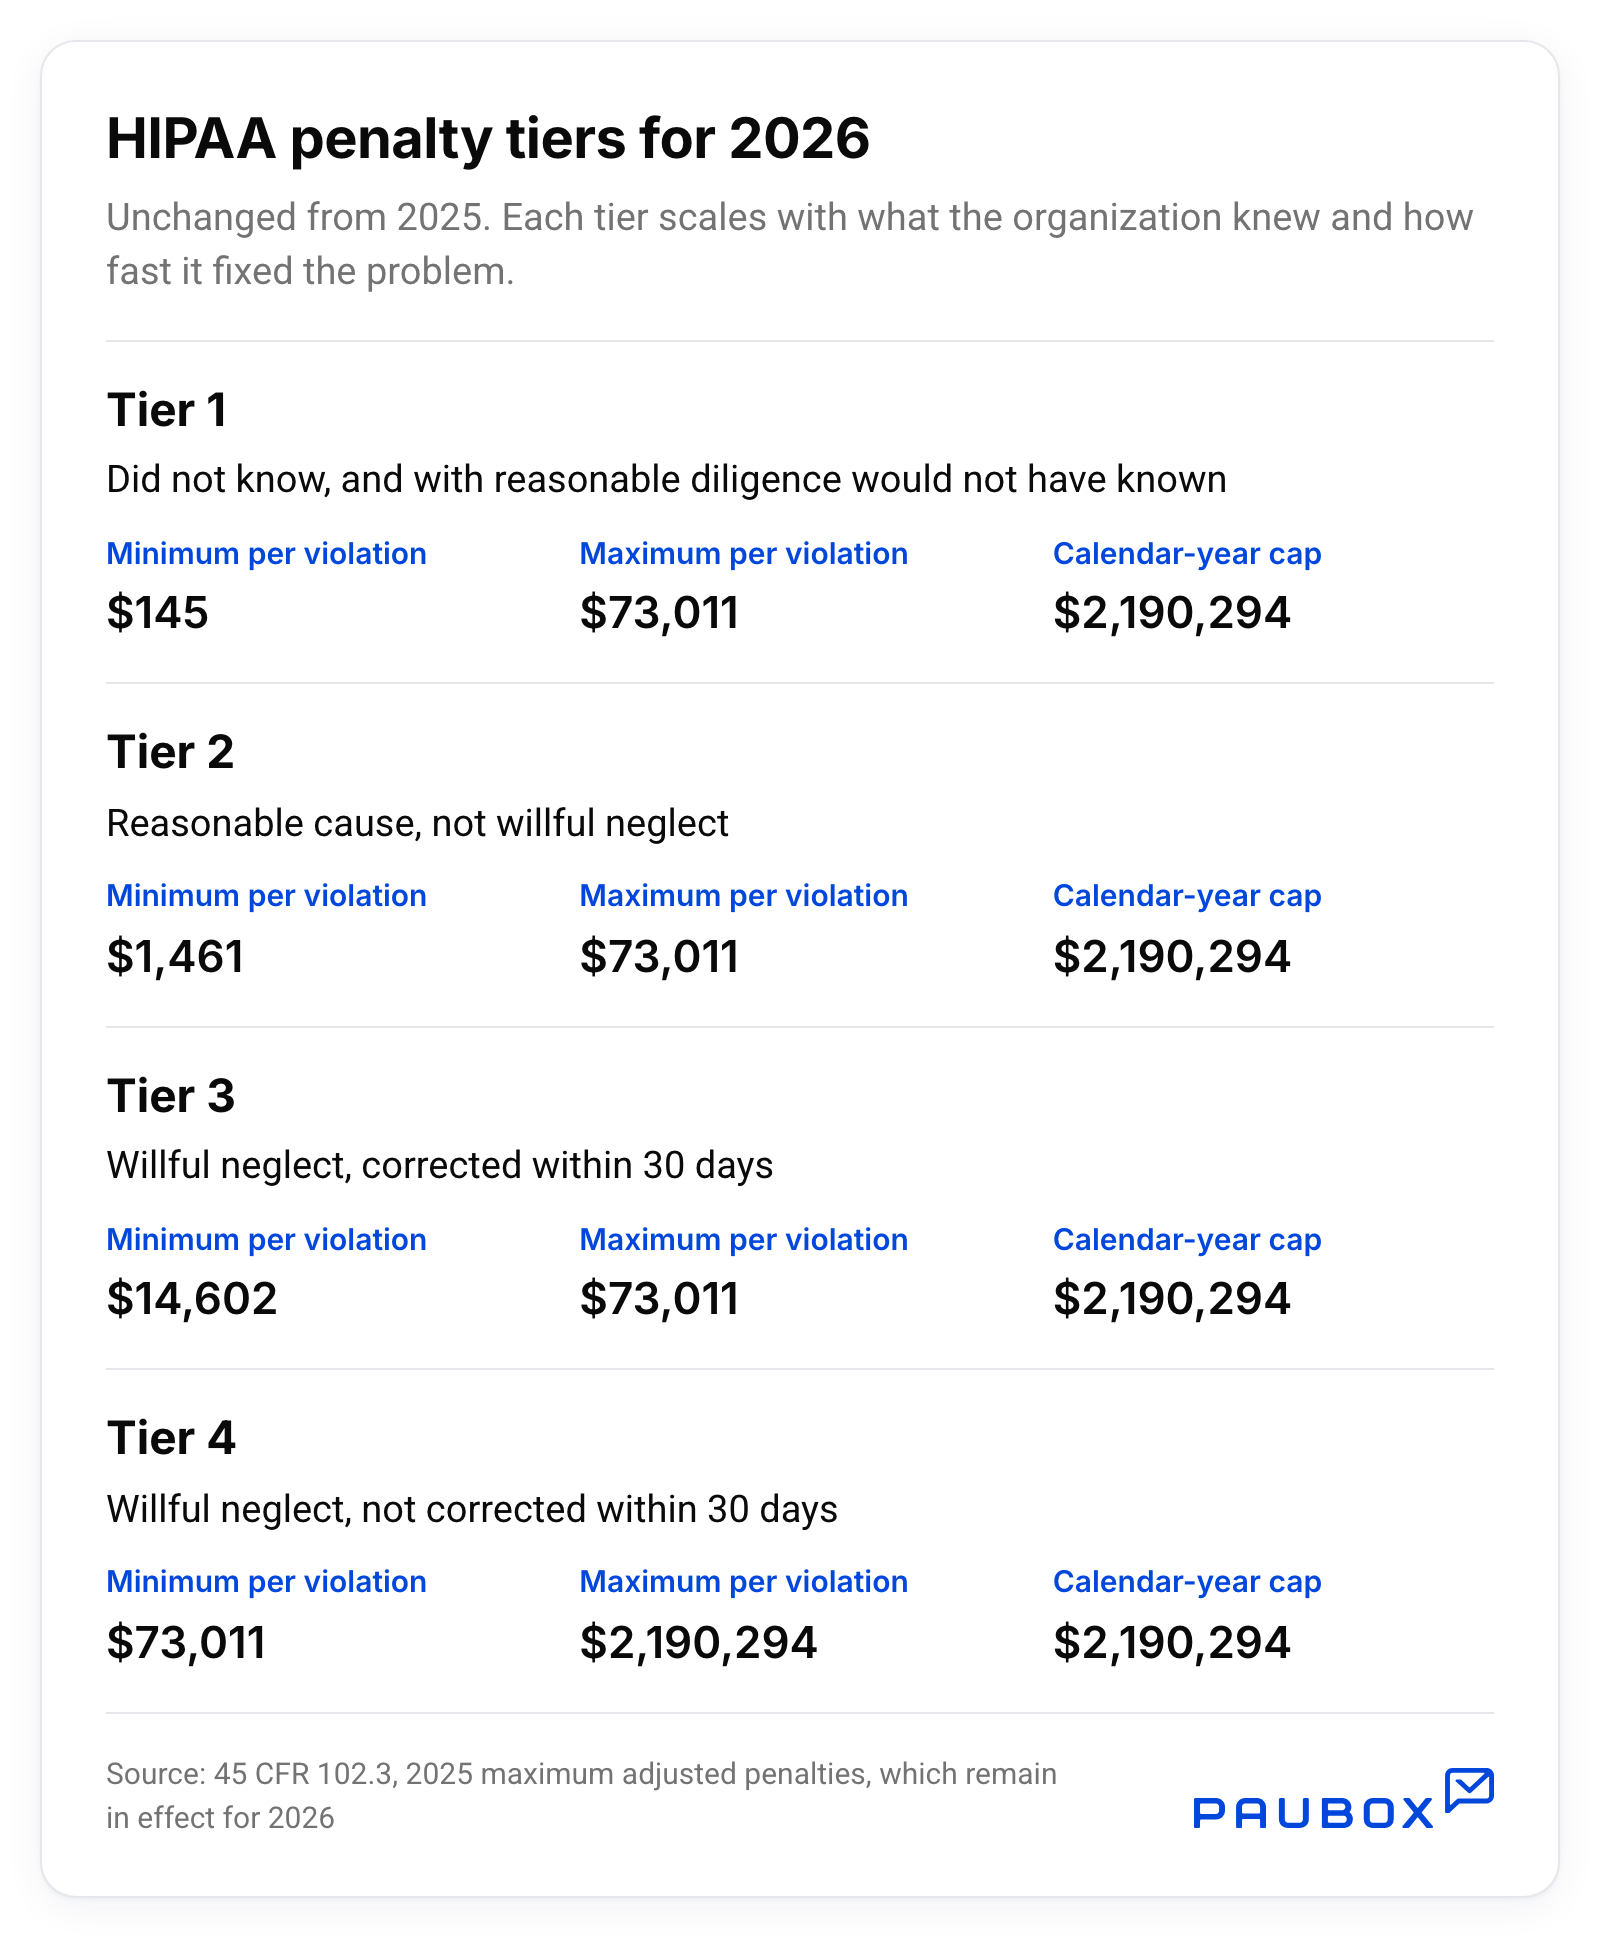
Source: 45 CFR 102.3, 2025 maximum adjusted penalties, which remain in effect for 2026.
In practice, OCR applies lower annual caps to the first three tiers under its 2019 Notification of Enforcement Discretion, which HIPAA Journal reports is still in use. Paubox covered how those caps work when HHS published the 2025 penalty adjustment.
Penalty pressure is heading up
OCR can impose exactly what it could before the notice, and the next adjustment is set to catch up: HIPAA Journal expects the 2027 multiplier to account for cost-of-living increases from 2025 through 2027, which would put two years of inflation into one step. HHS hasn't published the 2027 amounts yet.
The pressure runs the same way in Washington. HIPAA Journal reports that OCR has been pushing Congress to raise HIPAA penalties above HITECH Act levels, and enforcement didn't slow down while the amounts stood still.
OCR kept settling HIPAA cases in 2026
In April, OCR settled four ransomware investigations for a combined $1,165,000, bringing its Risk Analysis Initiative to 13 completed investigations. One of the four, Consociate Health, traced its ransomware breach back to a 2020 phishing attack.
In September, Ambry Genetics agreed to pay $700,000 after a phishing attack on one employee's email account potentially exposed the PHI of 225,370 people. Every entity in both announcements also agreed to a corrective action plan that OCR will monitor for two years.
"Email phishing is a common cyberattack that can lead to a breach of PHI and reveal HIPAA Security Rule deficiencies," said OCR Director Paula M. Stannard in the Ambry announcement.
Risk analysis failures appear in every one of these settlements
OCR cited a failure to conduct an accurate and thorough risk analysis in all five settlements above. For a compliance officer, that makes the risk analysis a sensible first document to review, whatever happens to the dollar amounts.
A few checks follow directly from OCR's own recommendations in those announcements:
- Confirm your risk analysis is current and maps how ePHI enters and leaves your organization, including through email.
- Check that your HIPAA compliant email setup encrypts ePHI in transit, one of OCR's listed safeguards.
- Document when you find and correct a violation, since the line between Tier 3 and Tier 4 depends on correction within 30 days.
For more on how OCR weighs culpability, see Paubox's guide on how to determine the severity of a HIPAA violation.
Go deeper: Get your security house in order before the new year, a Paubox webinar on November 11, 2026, at 10 a.m. PT.
